User
kato
7 specs on Spekkr.
-
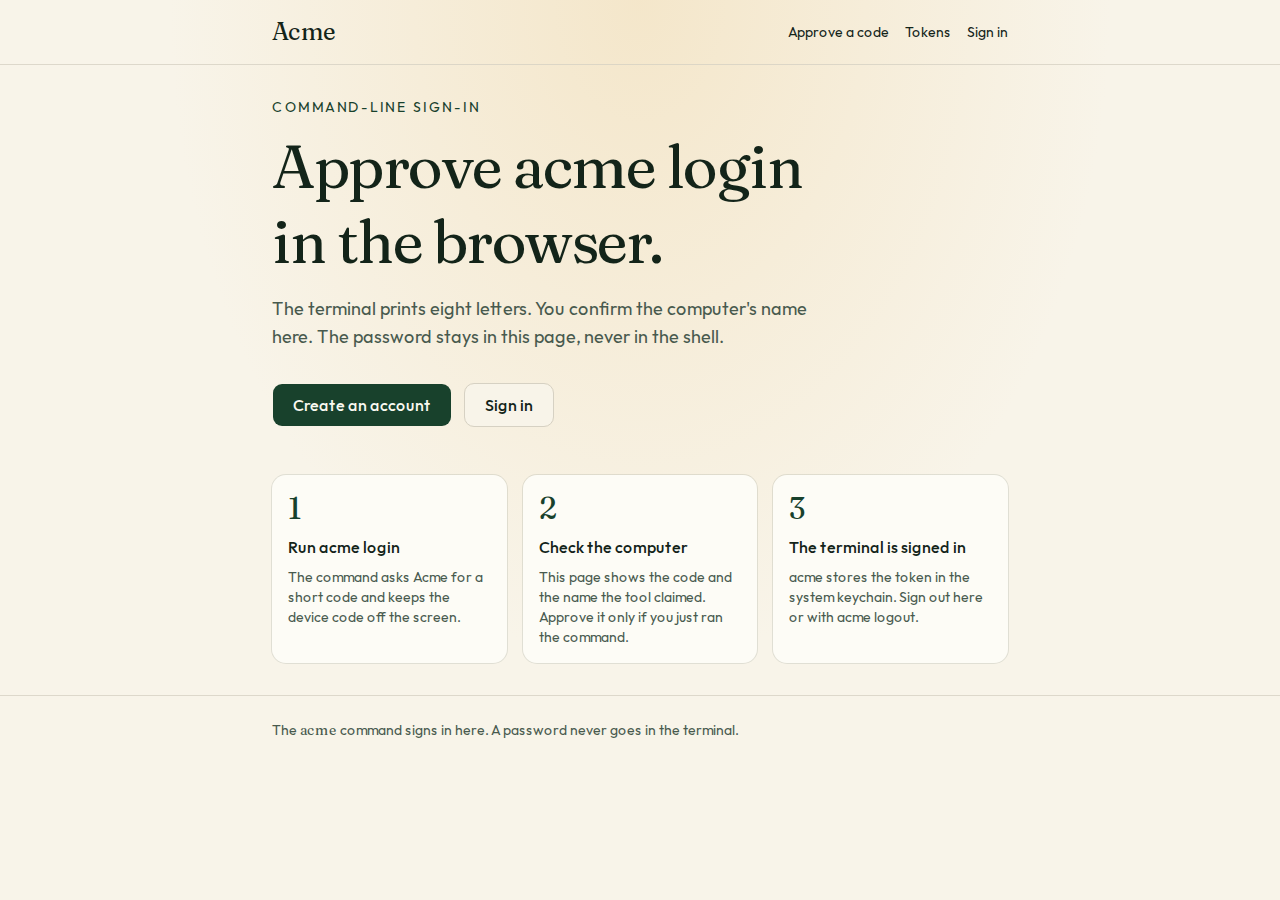 Sign-in for a command-line tool
Let a command-line tool sign in through the browser with a short code, keep its token in the system keychain and sign out cleanly.
-
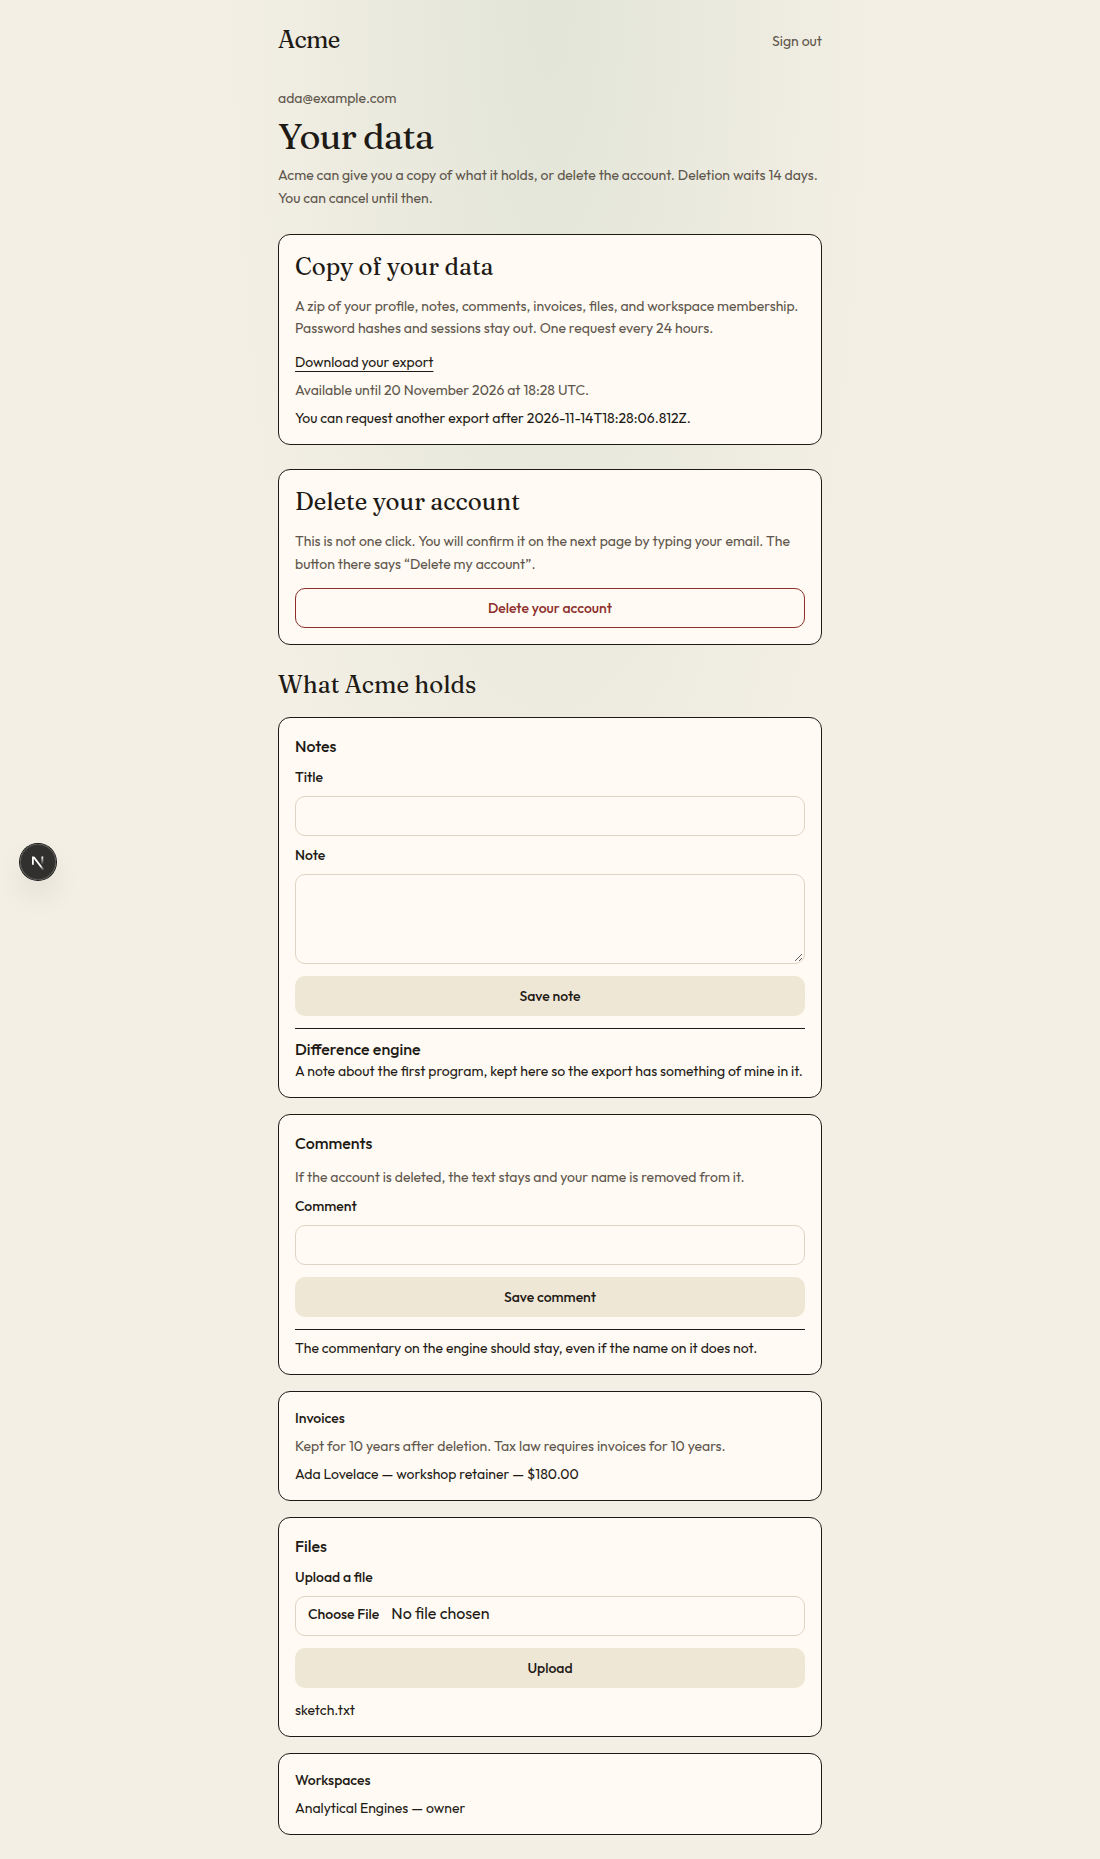 Data export and account deletion
Let people download what you hold about them and delete their account, with a grace period and a test that nothing is left behind.
-
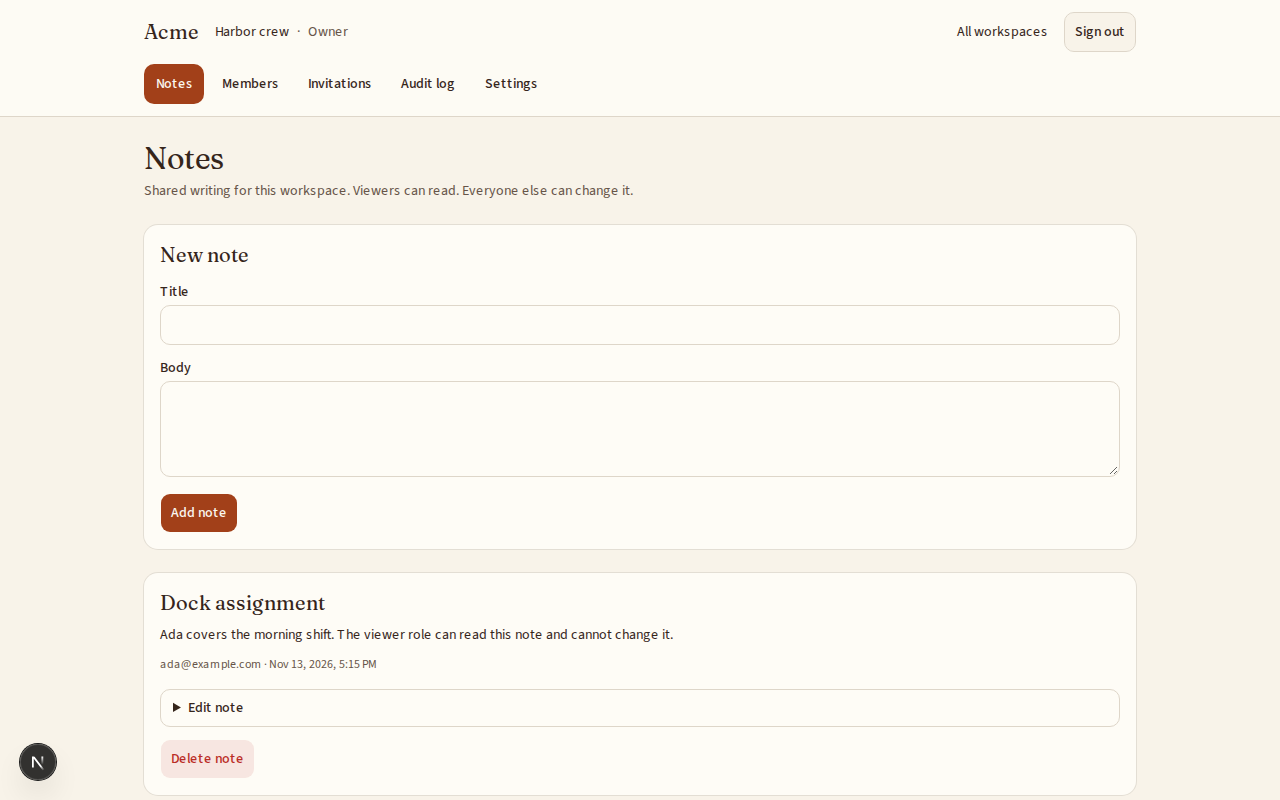 Team accounts and permissions
Workspaces, roles, invitations and an audit log for a multi-tenant app, with a test for every permission rule.
-
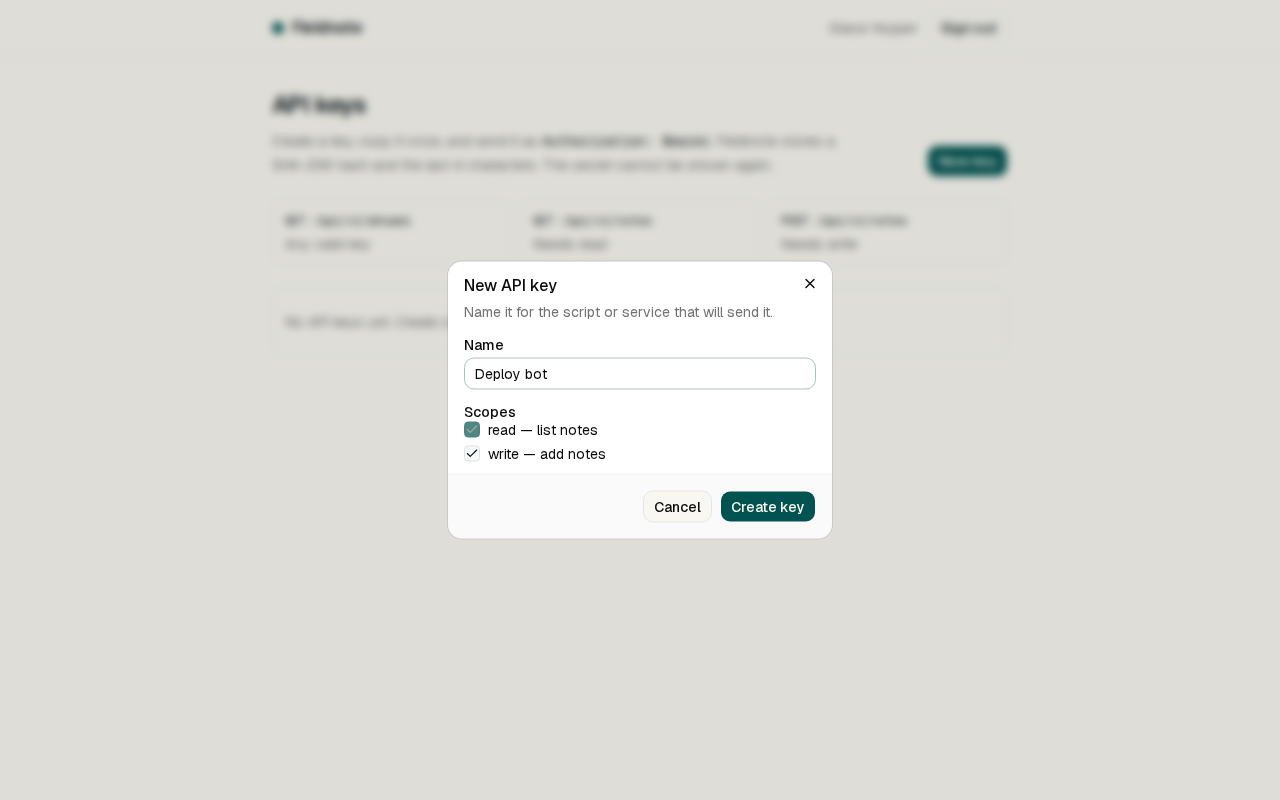 API keys
Keys your customers create to call your API: shown once, stored as hashes, with scopes, rotation and a last-used time.
-
 Two-factor sign-in
A second sign-in step with authenticator-app codes and recovery codes, added to the sign-in an app already has.
-
 Sign in with Google or GitHub
Sign-in through Google and GitHub, with linking rules that cannot be used to take over someone else's account.
-
 Sign-in with email
Sign-up, sign-in by password or emailed link, sessions and password reset, with a test for every way an account can be taken over.